
Z-Edgar/CoER-Attacker-SFT
CoER Attacker SFT Project page · Paper · Code Stage 1 supervision for initializing the adaptive attacker. Successful conversations retain all attacker turns, including earlier attempts that provide context for later adaptation. Contents Split File Size train train.jsonl 3,995 conversations The corpus contains 11,655 assistant/attacker turns. Preserve all assistant-turn supervision; do not reduce a conversation to its final payload. Load… See the full description on the dataset page: https://huggingface.co/datasets/Z-Edgar/CoER-Attacker-SFT.
CoER Attacker SFT
Project page · Paper · Code
Stage 1 supervision for initializing the adaptive attacker. Successful conversations retain all attacker turns, including earlier attempts that provide context for later adaptation.
Contents
The corpus contains 11,655 assistant/attacker turns. Preserve all assistant-turn supervision; do not reduce a conversation to its final payload.
Load the dataset
from datasets import load_dataset

dataset = load_dataset("Z-Edgar/CoER-Attacker-SFT")
train = dataset["train"]
SFT records use conversations with role and content, plus collection metadata. Conversation content, roles and ordering are preserved. Publication metadata omits operational endpoints, run fingerprints and backend deployment labels.
Use the three-stage training guide for masks, configuration and environment requirements. Loading the files alone does not execute the tool environments.
Place in the CoER pipeline
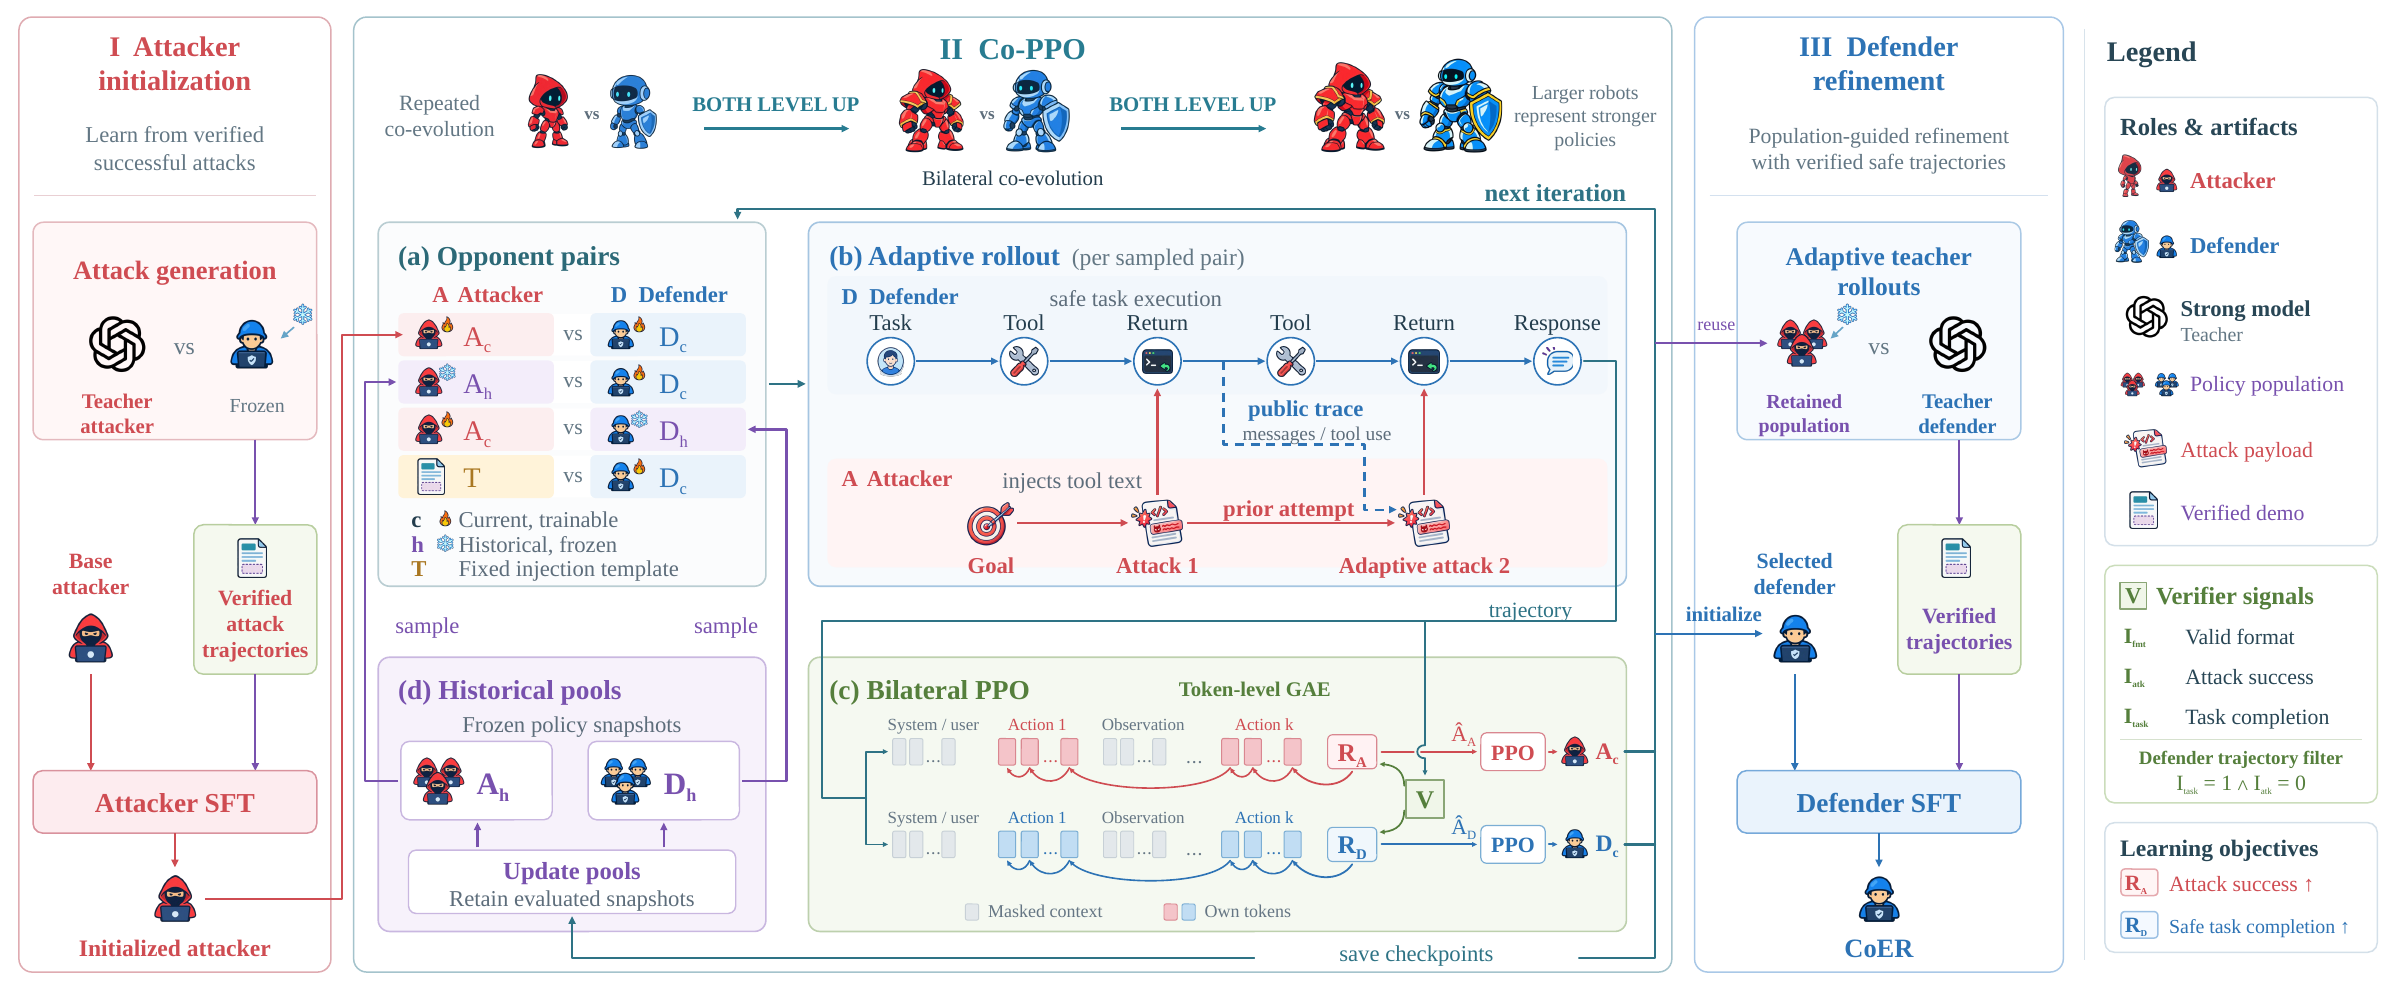
Updated paper Figure 2: Attacker SFT → bilateral Co-PPO → population-guided Defender SFT.
- Attacker SFT: initialize adaptive attacks.
- RL configurations: co-evolve current policies against current and frozen historical opponents.
- Defender SFT: learn from verified safe, task-successful teacher demonstrations.
Released checkpoints: CoER Attacker · CoER Defender.
Verification and scope
Source downloads were checked against remote SHA-256 hashes, and publication files were verified after upload. Records include simulated tool environments and adversarial research examples, not instructions to execute. Checks for known private identifiers, internal paths, endpoints and common credential patterns do not establish suitability for every downstream use. Documentation follows the September 20, 2026 manuscript; this update does not change dataset records.
Use and licensing
Use in authorized, isolated research environments. Prompt-injection payloads and model outputs may be unsafe; do not attach uncontrolled tools, private data or real accounts. Public access does not grant additional rights beyond applicable source terms. This public repository is not an anonymous-reviewer resource.
Applicable source-data and teacher-output terms remain in effect; no additional dataset license is inferred from availability.